As the January 1, 2027, deadline for payment data localisation rapidly approaches, Nigeria’s financial services sector finds itself at a critical crossroads. Commercial banks, merchant acquirers, payment service providers, and fintech startups are being forced to fundamentally re-evaluate how they architect, store, secure, and govern sensitive customer and transactional records.
The impending regulatory directive from the Central Bank of Nigeria (CBN) represents much more than a routine compliance check or an administrative box-ticking exercise. It is a massive infrastructural and engineering overhaul that touches upon every layer of the digital financial ecosystem. Industry stakeholders are grappling with the complex reality of relocating core databases to domestic facilities while simultaneously maintaining uninterrupted access to cutting-edge global technology, ensuring high availability, and mitigating emerging systemic vulnerabilities such as concentration risk.
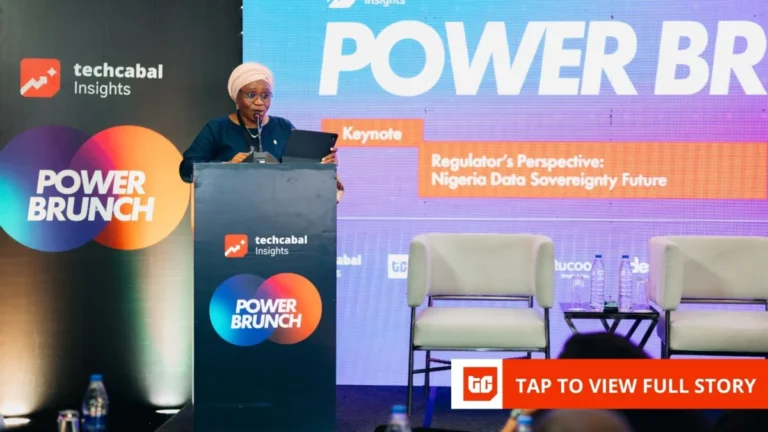
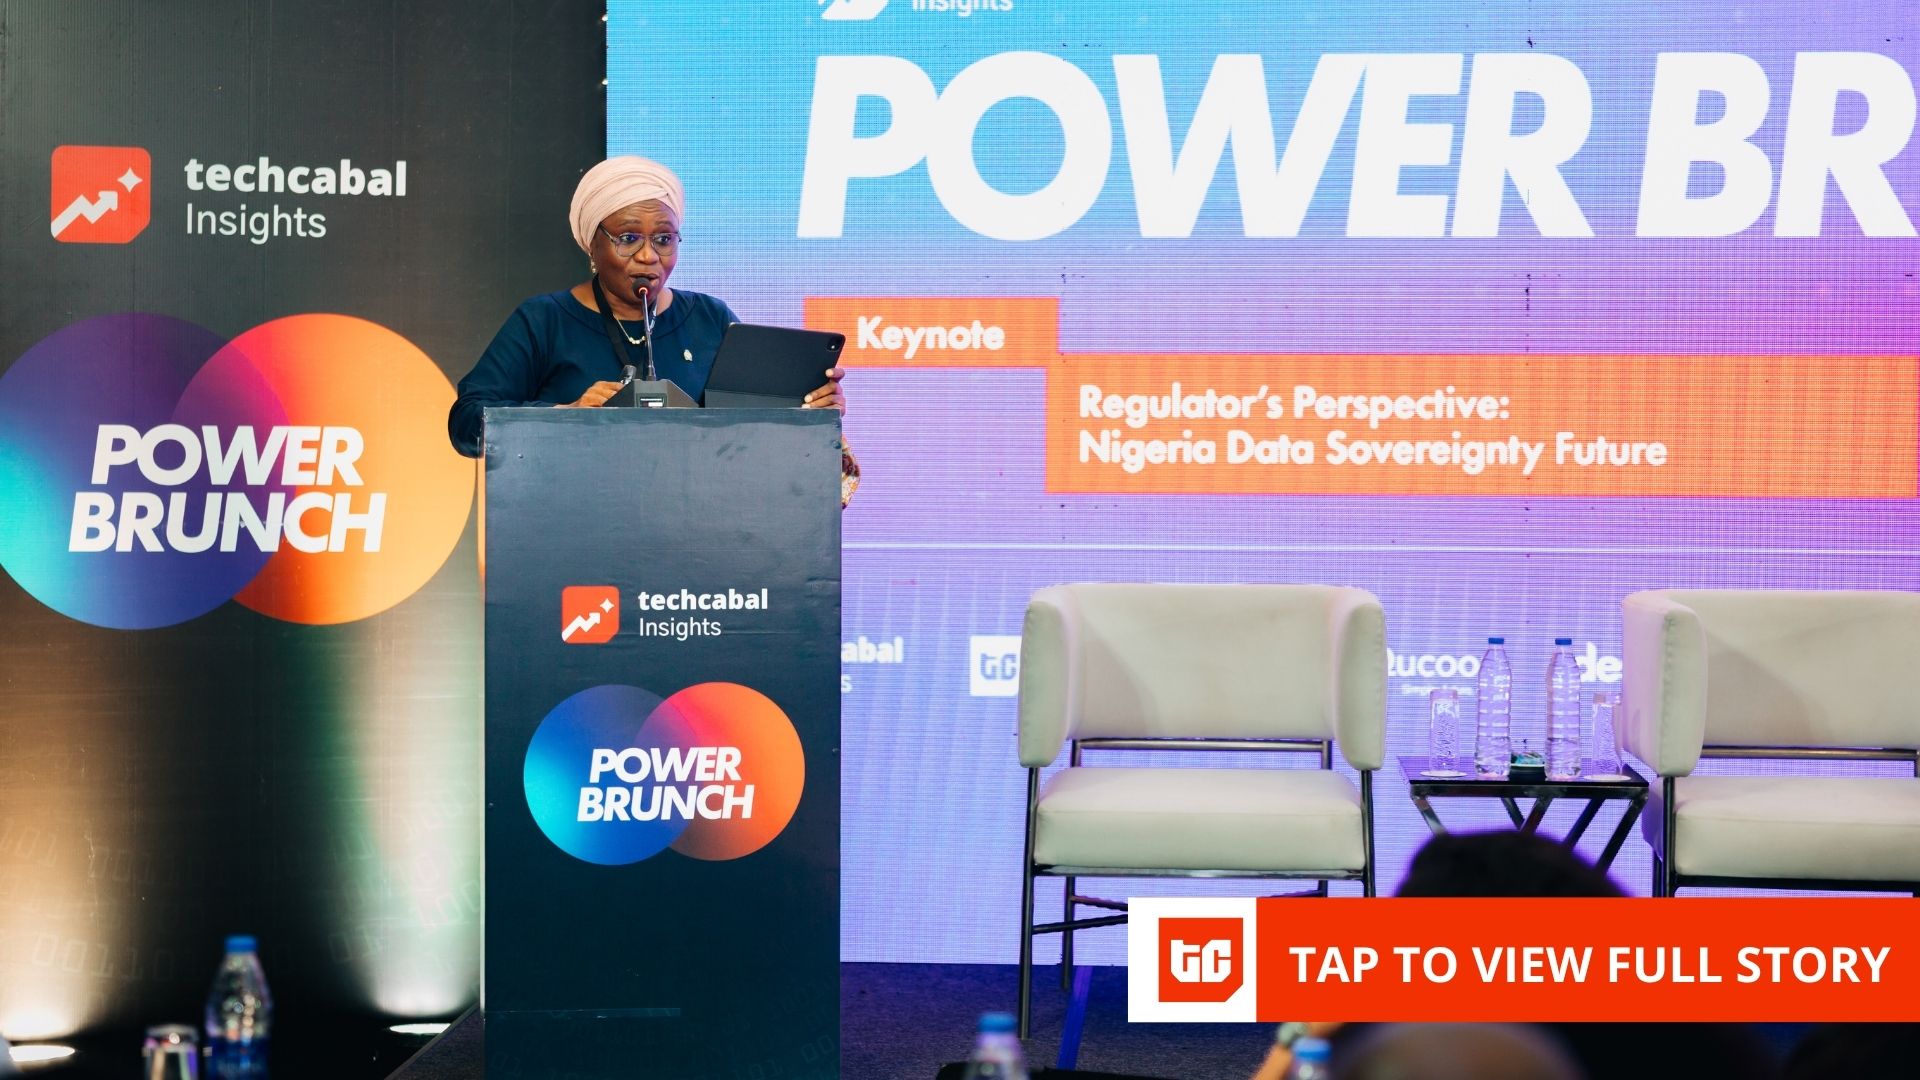
These intricate challenges took center stage during a series of high-level panel discussions at the TC Insights Power Brunch. Organised by TechCabal’s research and intelligence arm in strategic collaboration with Amazon Web Services (AWS), the event brought together prominent figures from banking, regulatory bodies, telecommunications, and cloud infrastructure to dissect the multi-layered implications of the forthcoming mandate. Discussions moved past superficial compliance metrics, probing deep into the operational, governance, and infrastructural realities that financial institutions must address before the strict implementation date arrives.
Beyond Real Estate: The Engineering and Governance Hurdles of Localisation
A central theme emerging from the industry dialogues is that data localisation is fundamentally an engineering and governance challenge rather than a simple real-estate mandate for server space. Simply relocating databases from foreign cloud regions to physical data centres located within Nigeria satisfies regulatory paperwork, but it does not inherently guarantee operational resilience, fault tolerance, or impenetrable security against sophisticated cyber threats and systemic market shocks.
Moving production environments locally without simultaneously overhauling legacy architectures can introduce significant operational hazards. Financial institutions must account for how transactional data flows across distributed networks, where it undergoes real-time transformation, how it is replicated across geographically disparate disaster-recovery clusters, and which third-party software vendors retain peripheral access or API keys.
Consequently, the mandate demands cross-functional collaboration. It is no longer an isolated mandate for the Chief Information Officer (CIO) or the IT department. Legal teams, regulatory compliance officers, cybersecurity heads, finance departments, product managers, and vendor management teams must work in unison. Such sweeping structural changes require explicit executive and board-level ownership to ensure that risk appetites align with the technical realities of domestic data storage.
Sovereignty Versus Isolation: Defining the Regulatory Objective
Throughout the discourse, regulators and industry experts alike sought to carefully delineate the boundary between national data sovereignty and technological isolationism. The primary objective of the Central Bank of Nigeria’s directive is not to sever the Nigerian financial sector’s longstanding ties with global hyperscalers, nor is it to force institutions to abandon robust international platforms in favor of unproven or fragile domestic alternatives.
Instead, the regulatory framework is designed to establish domestic oversight, legal jurisdiction, and visibility over core financial records. Policymakers aim to ensure that in the event of severe geopolitical disruptions, cross-border subsea cable cuts, or international trade disputes, domestic financial transactions can continue to be processed, validated, and audited within the national borders.
This nuanced approach mirrors how broader digital infrastructure initiatives are already unfolding across Nigeria’s public sector. Government agencies have consistently demonstrated that national sovereignty can coexist with strategic partnerships involving global technology giants. For instance, the Economic and Financial Crimes Commission (EFCC) maintains active collaborations with Microsoft to deploy advanced cloud-based artificial intelligence and machine-learning analytics for financial crime detection. Similarly, the Federal Ministry of Education partners extensively with Amazon Web Services to drive cloud computing and AI certification programs across federal and state tertiary institutions. Furthermore, state-owned digital infrastructure provider Galaxy Backbone Limited maintains deep technical partnerships with global ICT leader Huawei.
For Nigeria’s banking and fintech ecosystem, the operational takeaway is unambiguous: achieving tighter domestic control over critical data does not require sacrificing access to the scalability, security features, and processing power of global cloud environments. The ultimate goal is to pioneer a hybrid or localized model that reinforces national oversight while keeping the country firmly plugged into the global innovation grid.
The Infrastructure Paradox: Power, Fibres, and Resilience
Enforcing mandatory local data storage inevitably highlights pre-existing structural deficits within Nigeria’s foundational infrastructure. Building or leasing a local server room or data centre provides negligible security if the broader ecosystem suffers from unreliable public power grids, limited fibre-optic redundancy, and a scarcity of geographically diverse disaster-recovery facilities.
This creates a delicate infrastructure paradox. On one hand, Nigeria urgently requires robust, high-capacity domestic infrastructure capable of handling high-volume financial transactions without latency spikes. On the other hand, the financial sector cannot afford to be abruptly cut off from the expansive scale, advanced security tooling, and global redundancy models offered by international cloud platforms.
Industry consensus points to a collaborative path forward. International technology providers can—and likely must—remain active participants in the ecosystem, provided that the physical and virtual services supporting critical financial institutions strictly adhere to rigorous local standards for security, resilience, sovereignty, and regulatory visibility.
Furthermore, this policy shift has the potential to act as a powerful economic catalyst, unlocking a massive domestic infrastructure market. It is expected to spur unprecedented demand for Tier-3 and Tier-4 data centres, enterprise-grade cloud services, resilient telecommunications connectivity, advanced cybersecurity solutions, systems integration, and specialized technical skill sets. However, the realization of these investments hinges heavily on regulatory clarity. Financial institutions continue to seek definitive guidance regarding hybrid cloud architectures, cross-border data processing permissions, third-party vendor arrangements, and precise classifications of which peripheral datasets fall within the strict residency requirements.
Phase One of Compliance: Comprehensive Data Mapping
Before any physical data migration or database re-architecting begins, financial institutions must undertake exhaustive data mapping exercises to avoid costly configuration failures, compliance breaches, or operational downtime.
A comprehensive data audit must systematically trace the complete lifecycle of payment information. Institutions need to identify precisely where every data point originates, how and where it is transformed during transaction processing, the pathways it takes as it replicates across fallback clusters, and which external microservices or third-party vendors hold access privileges.
This mapping must extend far beyond primary databases to encompass unstructured metadata, system audit logs, application state files, operational workflows, and the various auxiliary systems that orbit core payment gateways. By establishing a clear compliance baseline and conducting thorough Data Privacy Impact Assessments (DPIAs), organisations can adopt a calculated, risk-based approach to determine the exact infrastructure architecture that suits their institutional objectives before sequencing their migration timelines.
Navigating Concentration Risk and Systemic Vulnerabilities
As institutions rush to comply with the 2027 deadline, a new systemic hazard is beginning to take shape: concentration risk. If a significant majority of Nigeria’s tier-1 banks and high-growth fintechs choose to migrate their core databases and workloads to the exact same domestic infrastructure providers or local data centre operators, the financial system could inadvertently trade geographic vulnerability for localised systemic risk.
An outage, cyber incident, or physical disruption at one of these dominant local facilities could instantly cripple a vast portion of the nation’s payment rails, freezing interbank transfers, point-of-sale transactions, and mobile banking applications simultaneously.
To mitigate this looming threat, industry experts emphasize that localisation must be treated primarily as an exercise in structural resilience rather than a mere compliance checkbox. Financial institutions must diversify their infrastructure dependencies, implement multi-cloud or hybrid-local failover strategies, and establish rigorous stress-testing protocols to ensure operational continuity under worst-case scenarios.
Looking Ahead to 2027 and Beyond
As the countdown to January 1, 2027, continues, the pressure is squarely on executive boards and technology leaders within Nigeria’s financial sector. The mandate represents a defining moment for the maturation of the country’s digital economy.
Successfully navigating this transition will require unprecedented cooperation between financial regulators, commercial institutions, telecommunications providers, and global hyperscalers. Those institutions that view the mandate not as an administrative burden, but as a strategic opportunity to modernize their data governance frameworks, fortify their cybersecurity postures, and build genuinely resilient infrastructures, will emerge as the undisputed leaders of Africa’s evolving financial technology landscape.